 Skip to content
Trusted audit advisory,
built for cyber resilience.
Ten-X Consulting is a trusted consulting firm specializing in Audit advisory, Cybersecurity, IT Auditing, Risk assessment, Compliance services, training workforce and IT Certifications for organizations.
We are dedicated to helping businesses stay ahead of cyber threats by ensuring their IT environments remain secure, compliant, and resilient — and also ensuring the effectiveness of controls in financial and business operations.
- Cybersecurity Audit
- ISMS Audit (ISO 27001)
- PCI DSS Audit
- NDPA / DPIA Audit
- Certification Audit
- AML/CFT Assessment
- Financial & Operational Audit
- IT Strategy & Digital Transformation
- Business Continuity & Disaster Recovery
- IT Governance & Risk Management
- Information Security & GRC Consulting
- Vulnerability Assessment & Penetration Testing
- ISO 27001 LI/LA
- BCMS ISO 22301
- Cybersecurity Awareness Training
- CISM Exam Prep
Certified Information Security Manager
A focused four-week intensive built to take you from concept to confidence — everything you need to sit the CISM exam and lead information security at the management level.
October cohort: 3 – 31 Oct 2026 · New cohorts run monthly
Information Security Governance
Aligning strategy with enterprise goals and leadership.
Information Security Risk Management
Identifying, assessing and treating organisational risk.
Information Security Programme Development
Building and resourcing a security programme.
Incident Management
Preparing for, responding to and recovering from security incidents.
Who should attend
- IT & information security managers
- Risk, audit and compliance officers
- Professionals preparing for the CISM exam
- Anyone moving from technical to managerial security roles
Seats for the next CISM cohort are limited.
Register your interestOur Services
From audit and assurance to hands-on training, we scope engagements around the systems and controls you actually depend on.
Audit and Assurance
Cybersecurity Audit · ISMS Audit (ISO 27001) · PCI DSS Audit · Nigeria Data Protection Act (NDPA) / DPIA Audit · Certification Audit · AML/CFT Assessment · Financial and Operational Audit.
Details →Training & Development
ISMS ISO 27001 LI/LA, BCMS ISO 22301 · Cybersecurity Awareness · Workshops, Seminars and Webinars · Knowledge Sharing Sessions.
Details →IT Audit Advisory
IT Strategy and Digital Transformation · Business Continuity & Disaster Recovery Planning · IT Governance and Risk Management · Framework and Policies Development.
Details →Consultancy
Information Security and GRC Consulting · IT Security Consulting · IT Service Management Consulting · Vulnerability Assessment and Penetration Testing · Business and Operational Audit.
Details →Ten-X Academy
Hands-on cybersecurity training for individuals and teams — built from the same frameworks we use in client engagements, not generic slide decks.
Introduction to Cybersecurity
A foundation course for anyone starting out — how attacks actually happen, the core principles of confidentiality, integrity and availability, and the vocabulary you need to follow any security conversation.
Learn more →
Ethical Hacking Essentials
An introduction to offensive security — how penetration testers think, the stages of a real engagement, and the legal and ethical boundaries that separate a tester from an attacker.
Learn more →
Governance, Risk & Compliance (GRC)
How organizations actually manage security as a business function — building policy, running risk assessments, and mapping controls to frameworks like ISO 27001 and the Nigeria Data Protection Act.
Learn more →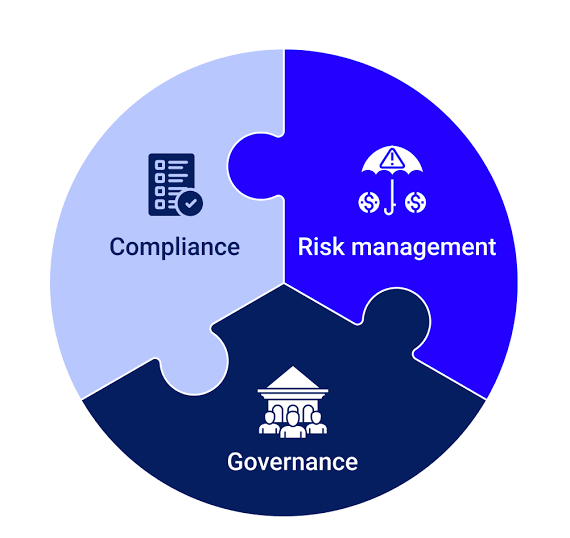
Introduction to Security Operations
A first look inside the SOC — how alerts are triaged, what a security analyst actually monitors day to day, and the tools behind detection and incident response.
Learn more →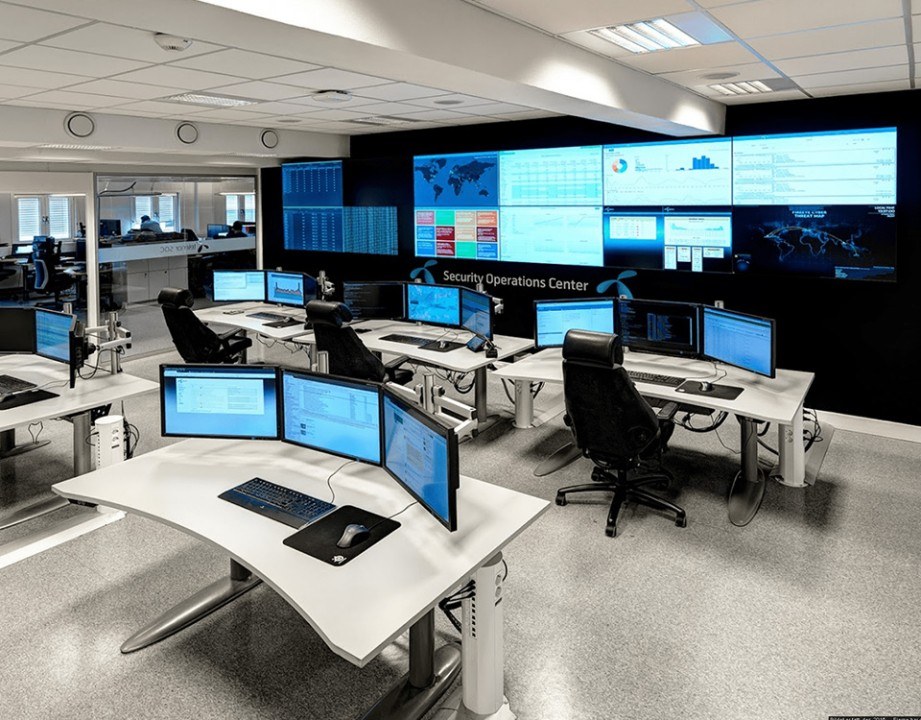
Certified Information Security Manager (CISM)
The globally recognised ISACA credential for professionals who manage, design and oversee an organisation's information security. Our four-week live intensive is exam-focused, built to take you from concept to confidence.
Learn more →
Want to run one of these as a cohort for your team?
Talk to us about trainingVision & Mission
To be the premier partner for businesses seeking to navigate and mitigate cyber threats, IT regulatory compliance, business process re-engineering and ensuring a secure and resilient digital environment for all clients.
At Ten-X Consulting, we empower organizations by providing trusted advisory services, innovative cybersecurity training, and proactive IT compliance support — transforming workforces into the first line of defense against evolving threats and simplifying compliance for growth.
Core Values
Security
We prioritize safeguarding our clients' assets and data, ensuring robust protection against cyber threats.
Excellence
We strive for the highest standards in our services, continually seeking to improve and innovate.
Collaboration
We believe in the power of teamwork, working closely with clients and partners to achieve shared goals.
Understanding
We take the time to comprehend the unique challenges and needs of each client, tailoring solutions accordingly.
Reliability
We are a dependable partner, consistently delivering on our promises and maintaining trust.
Empowerment
We empower our clients and their teams with knowledge and tools to proactively defend against threats.
Let's talk about your compliance and security needs.
Reach out and our team will come back with a scoped proposal for your business.