 Skip to content
Practical cybersecurity training for people and teams.
Hands-on cybersecurity training for individuals and teams — built from the same frameworks we use in client engagements, not generic slide decks.
Introduction to Cybersecurity
A foundation course for anyone starting out — how attacks actually happen, the core principles of confidentiality, integrity and availability, and the vocabulary you need to follow any security conversation.
What you'll learn
- How common attacks work — phishing, malware, ransomware and social engineering
- The CIA triad: confidentiality, integrity and availability
- Everyday defences — strong authentication, patching, backups and safe habits
- How security fits into a business: roles, policies and frameworks
- The vocabulary to follow, and join, any security conversation
Ethical Hacking Essentials
An introduction to offensive security — how penetration testers think, the stages of a real engagement, and the legal and ethical boundaries that separate a tester from an attacker.
What you'll learn
- How penetration testers think and plan an engagement
- The stages of a test: reconnaissance, scanning, exploitation and reporting
- Hands-on labs in a safe, controlled environment
- The legal and ethical boundaries of testing
- Turning findings into clear, actionable reports
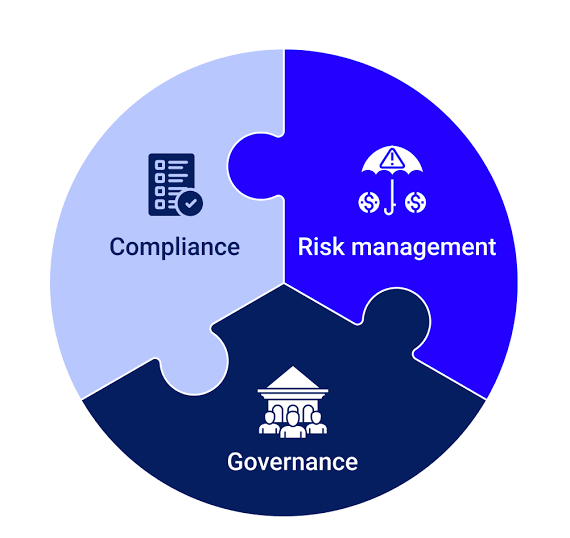
Governance, Risk & Compliance (GRC)
How organizations actually manage security as a business function — building policy, running risk assessments, and mapping controls to frameworks like ISO 27001 and the Nigeria Data Protection Act.
What you'll learn
- Writing and maintaining security policies people can actually follow
- Running a practical risk assessment
- Mapping controls to frameworks such as ISO 27001 and the Nigeria Data Protection Act
- Preparing for audits and reporting on compliance
- Governance: roles, accountability and management oversight
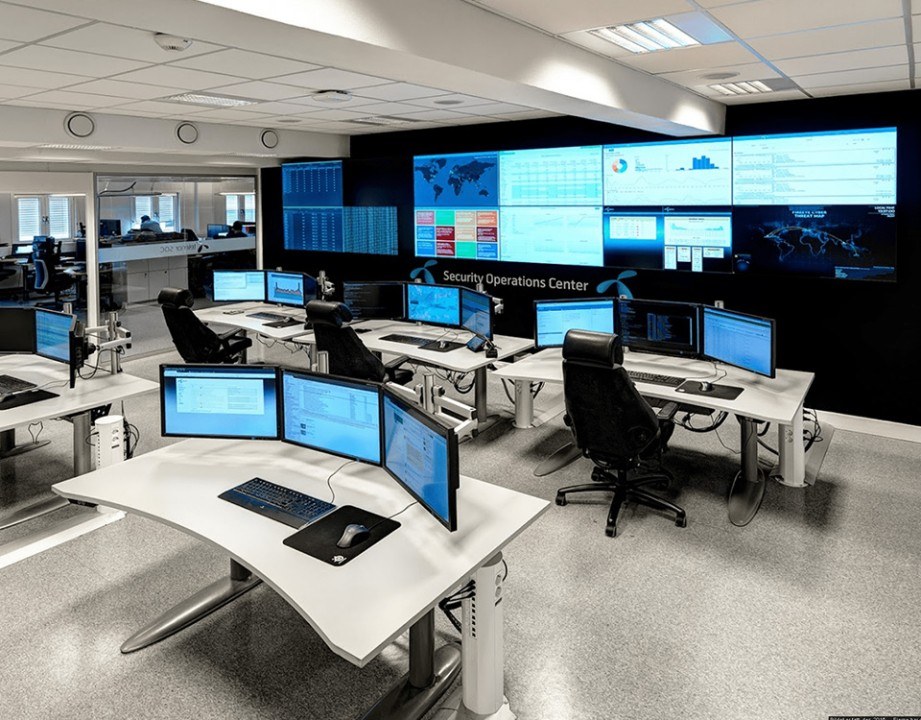
Introduction to Security Operations
A first look inside the SOC — how alerts are triaged, what a security analyst actually monitors day to day, and the tools behind detection and incident response.
What you'll learn
- What a Security Operations Center does, day to day
- How alerts are triaged — separating real incidents from noise
- The tools behind monitoring, detection and response
- The incident response lifecycle at a glance
- Career paths into SOC analyst roles
Certified Information Security Manager (CISM)
The globally recognised ISACA credential for professionals who manage, design and oversee an organisation's information security. Our four-week live intensive is exam-focused, built to take you from concept to confidence.
What you'll learn
- Information Security Governance — aligning strategy with enterprise goals and leadership
- Information Security Risk Management — identifying, assessing and treating organisational risk
- Information Security Programme Development — building and resourcing a security programme
- Incident Management — preparing for, responding to and recovering from security incidents
How to join a course
Individuals can enrol directly, and we can run any of these as a private cohort for your team.
Choose a course
Pick the course that matches your level and goals, or ask us which fits best.
Get in touch
Email or call us with the course and the number of people who want to attend.
Confirm your seat
We reply with the next start date and fees so you can secure your place.
Want to run one of these as a cohort for your team?
Talk to us about training